
MSP BUYER GUIDE
Security Assessment Report: From Priorities to a Priced Plan and Proof
A security assessment report is useful when it helps the reader decide what to do next. SCOUTz separates the owner’s priorities from operator evidence, task guidance and the dated checks needed to verify change.

EVIDENCE · INSIGHT · PROOF

What the client reads. What you work from.
Client copy
Plain-language findings, scope, unknowns and the next decision.
Operator copy
Evidence references, investigation steps, prerequisites, LOE and validation.
EVIDENCE · INSIGHT · PROOF
The same findings, packed for each meeting.
First meeting
Client-safe evidence, limits and discovery questions.
Win the deal
Priorities, a meeting pack and a scoped proposal.
Onboard
Owned work, dependencies and the incident playbook.
QBR
Dated changes, unresolved items and next decisions.
By Steve Copeland · Reviewed October 18, 2026. New guide; source article publication dates remain in their archived records.
Short answer
A security assessment report is useful when it helps the reader decide what to do next. SCOUTz separates the owner’s priorities from operator evidence, task guidance and the dated checks needed to verify change.
Make the next decision readable
The owner needs a plain-English account of the supported condition, possible consequence, missing context and recommended next question. Detailed evidence belongs where the technical reviewer can inspect it without overwhelming the business conversation.
A possible attack path is a scenario for review, not proof of an attack. The report should distinguish mapped signals, absent mapped signals and unassessed stages. A count needs its source and scope rather than a reassuring number alone.
Preserve the technical record
The operator version retains check IDs, sources, dates, investigation choices and technical steps. Fix guidance should explain what the condition is, why it matters, what to do next and how to verify the agreed change.
Client-safe output and operator output are not interchangeable. Keep named accounts, internal identifiers and restricted evidence with the authorized audience. White-label presentation does not remove those responsibilities.
Use the sample for what it actually demonstrates
The downloadable PDFs are anonymized, edited excerpts from first-party test assessments observed October 7, 2026. They are not complete customer reports, proof of customer outcomes or demonstrations of every current product capability.
The Microsoft 365 sample preserves actual unread states and visibility gaps. It is not an AI-readiness or Copilot-adoption verdict. Do not turn demonstration material into claimed live coverage or add unsupported scores to make it appear more complete.
Scope a proposal from the work plan
Phases group proposed tasks into This Week, This Month, This Quarter and Ongoing, with hour and dollar ranges. The MSP validates its own rate, dependencies and service mappings before quoting.
Studio Report Plays bundle suitable material for First meeting, Win the deal, Onboard and QBR. Consent still controls the evidence available. The visual Report Studio remains in validation.
Show what changed at the next review
A comparison can report resolved, changed, new and still-present findings. Keep the baseline date, new date, check identity and visibility limits alongside the result.
The insurance-question tally can organize movement between supported answers, gaps and confirmation needs. It does not decide insurance eligibility or establish full operational readiness. Ask for the customer-owned evidence that a scan cannot supply.
Client-Safe, Operator, and Microsoft 365 Views
ANONYMIZED APP-DERIVED EXCERPT
Anonymized, edited excerpts from existing first-party test assessments observed October 7, 2026. Identifiers and private values removed—not complete reports or customer-results proof.
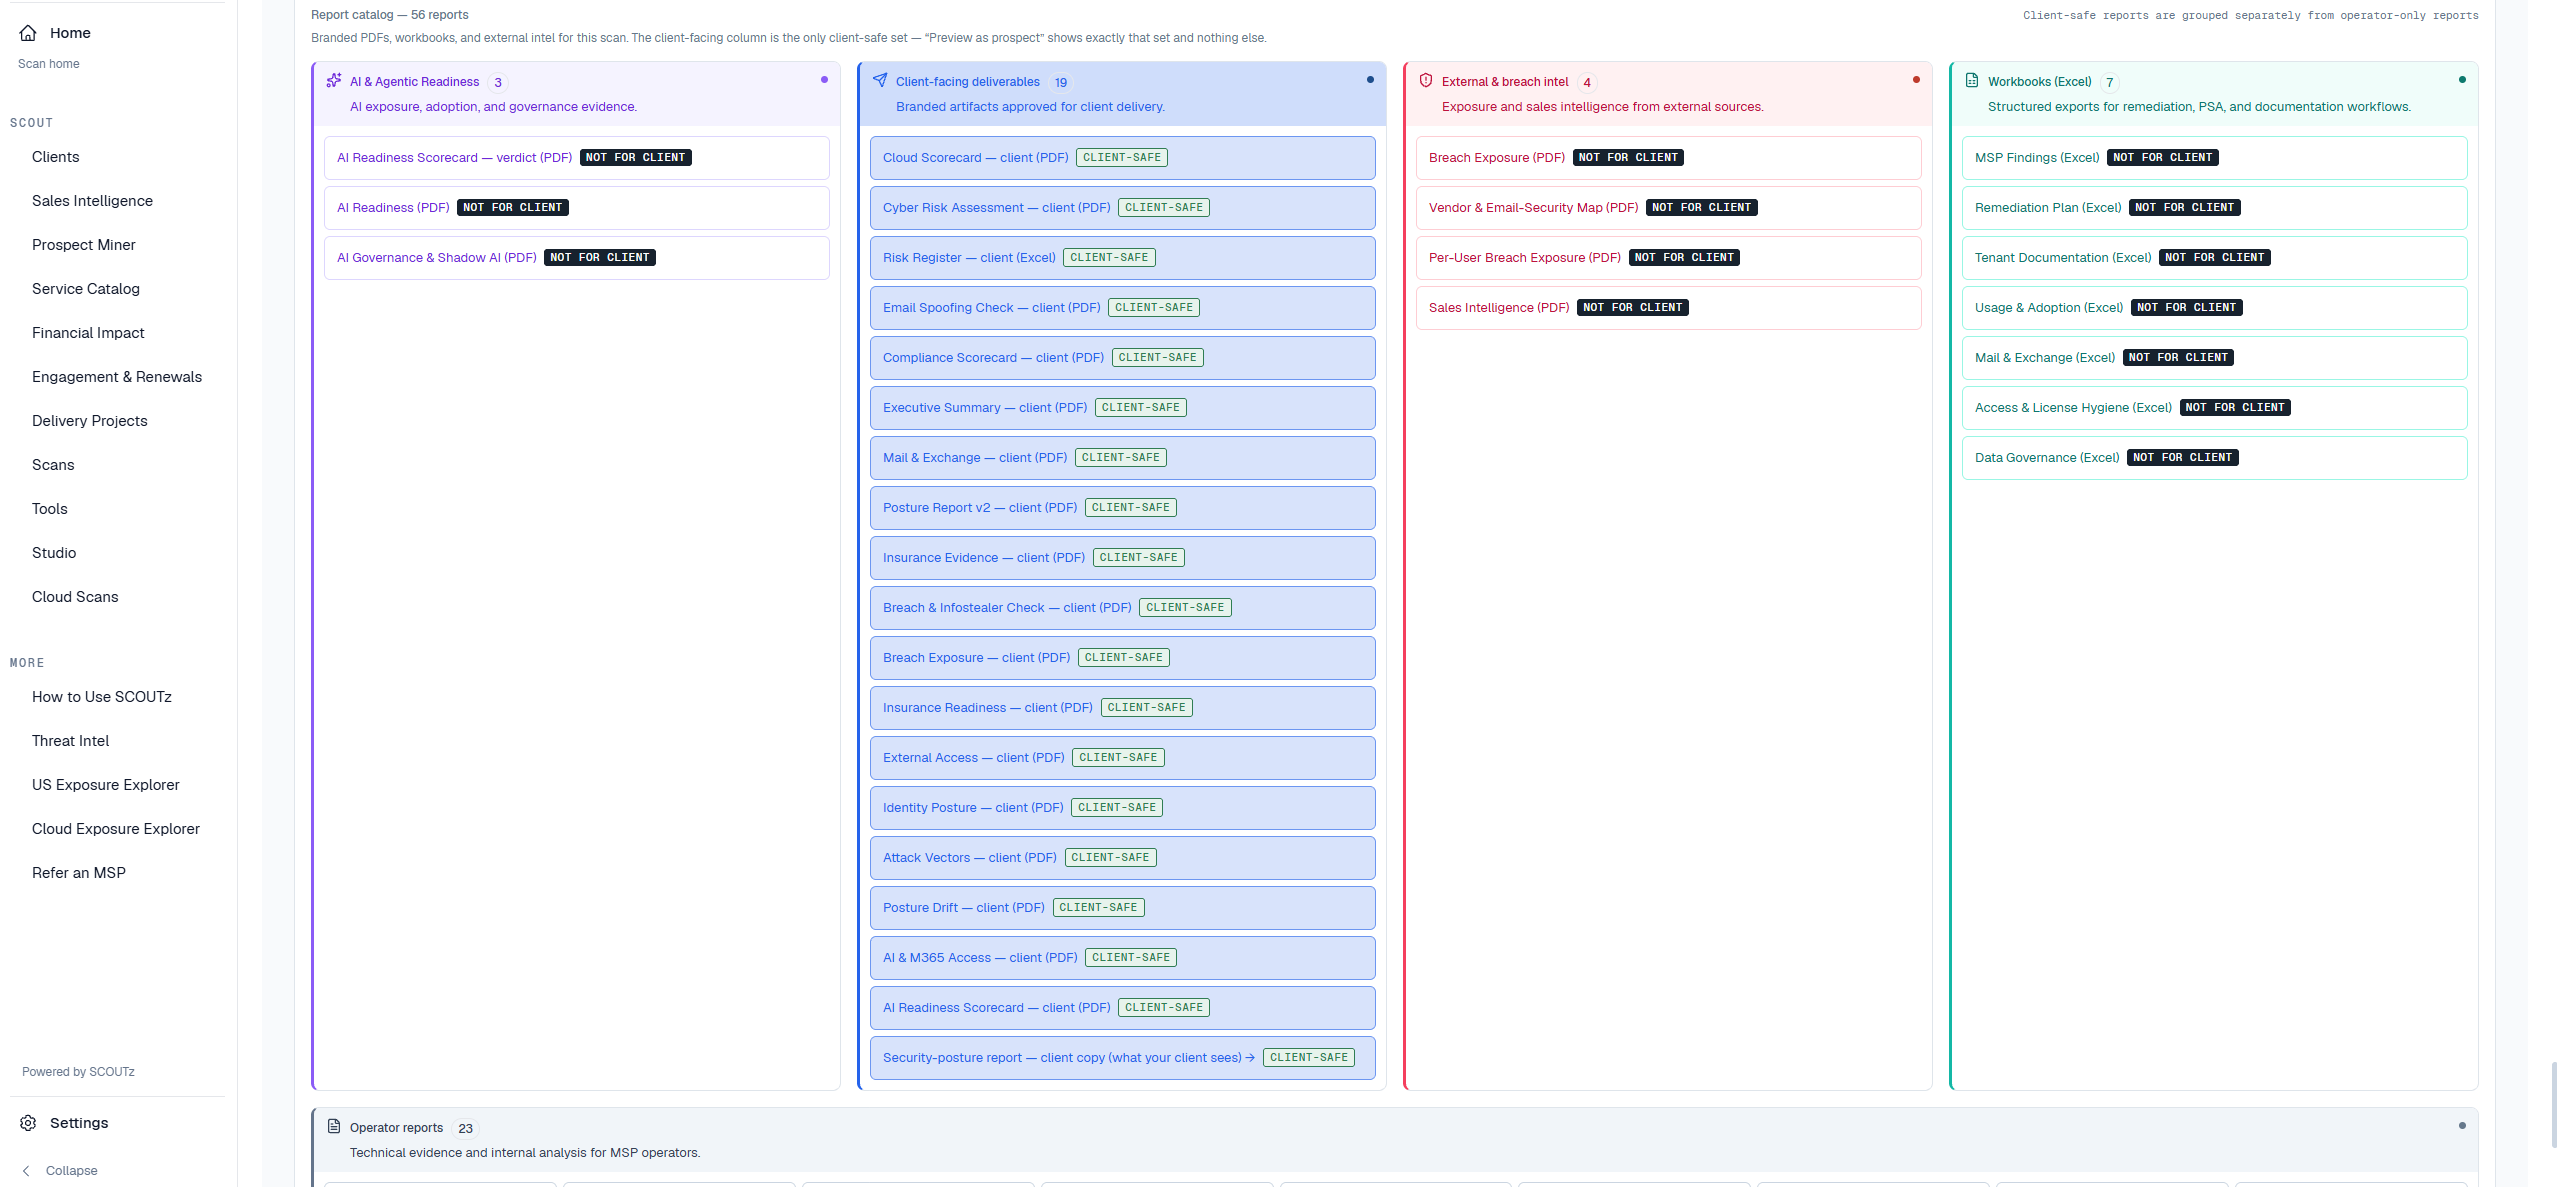
- Download the client-safe PDF excerpt
Selected stored public-source observations with source, date, limits and follow-up questions—not a security rating. This client-safe adaptation was edited from the operator report.
- Download the operator PDF excerpt
Edited excerpts of the operator record: sources, investigation choices and incomplete collector-coverage qualifications. Private values are omitted.
- Download the Microsoft 365 PDF excerpt
Selected cloud executive and AI excerpts preserve unread checks in Identity & Access and Perimeter, plus the DLP visibility gap. This is not an AI-readiness or Copilot-adoption assessment. Microsoft 365 NOT READ states remain visible.
The evidence behind the decision
35 public sources for a domain scan; 92 sources with read-only Microsoft 365 consent. Every report counts its checks and shows anything it couldn't read as unread, never as clean.
Microsoft 365 reviews require customer approval and read-only access. SCOUTz does not read mail, files, chats, documents or prompts, install an agent, or make changes.
In one example scan, the domain review read 17 checks; in one Microsoft 365 example, it read 174. Those are example results, not fixed coverage promises. Availability, permissions and source readability affect each run.
Deterministic checks decide findings, AI writes explanations and a human signs off. The MSP approves changes, performs delivery and determines whether the verification evidence is sufficient.
Frequently asked questions
What should a decision-ready security assessment report include?
It should connect supported priorities to actions, owners, estimate ranges, verification criteria and explicit limits. Preserve the source and date behind each important conclusion.
How do executive and technical reports differ?
The executive version supports business decisions in plain language. The technical version retains investigation details, checks and steps for the authorized operator.
Does the report include remediation costs?
The work plan supplies hour and dollar ranges as planning estimates. Your MSP validates rates, dependencies and scope before making a commercial commitment.
Can I white-label a report?
Yes. Client-facing output supports MSP branding, while audience restrictions and evidence limitations still apply.
Do the samples prove complete AI readiness?
No. The samples are edited excerpts, and the Microsoft 365 sample retains unread states. Readiness conclusions require documented criteria and customer-confirmed evidence.
How can I show what changed since the last report?
Compare dated evidence against the retained baseline with comparable scope and permissions. A missing result is not resolution when the source was unreadable.
Related guides and next steps
Start with a free public-domain score or discuss an authorized scenario in a demo. Open Beta applications remain human-reviewed; current commercial terms are on the pricing page.
Your next prospect meeting is already on the calendar.
Bring dated evidence, clear limits, and useful questions.