MARKETING + LEAD GEN
CYBERSECURITY PROSPECT INTELLIGENCE FOR MSPS
Walk into your next MSP prospect meeting with evidence.
You booked the meeting. Now give the buyer something specific to discuss.
SCOUTz turns dated public-source observations and customer-approved Microsoft 365 evidence into a clearer conversation: what was found, what it might mean and what to ask next.
Evidence → insight → proof. SCOUTz prepares the conversation. Your MSP owns the relationship and closes the deal.
30 days at $0 from provisioning·$279/month after·beta rate protected for 3 years from paid conversion
Built by RYTHMz for MSPs that want evidence before the pitch.
01 · FIND THE ACCOUNT02 · FIND THE REASON
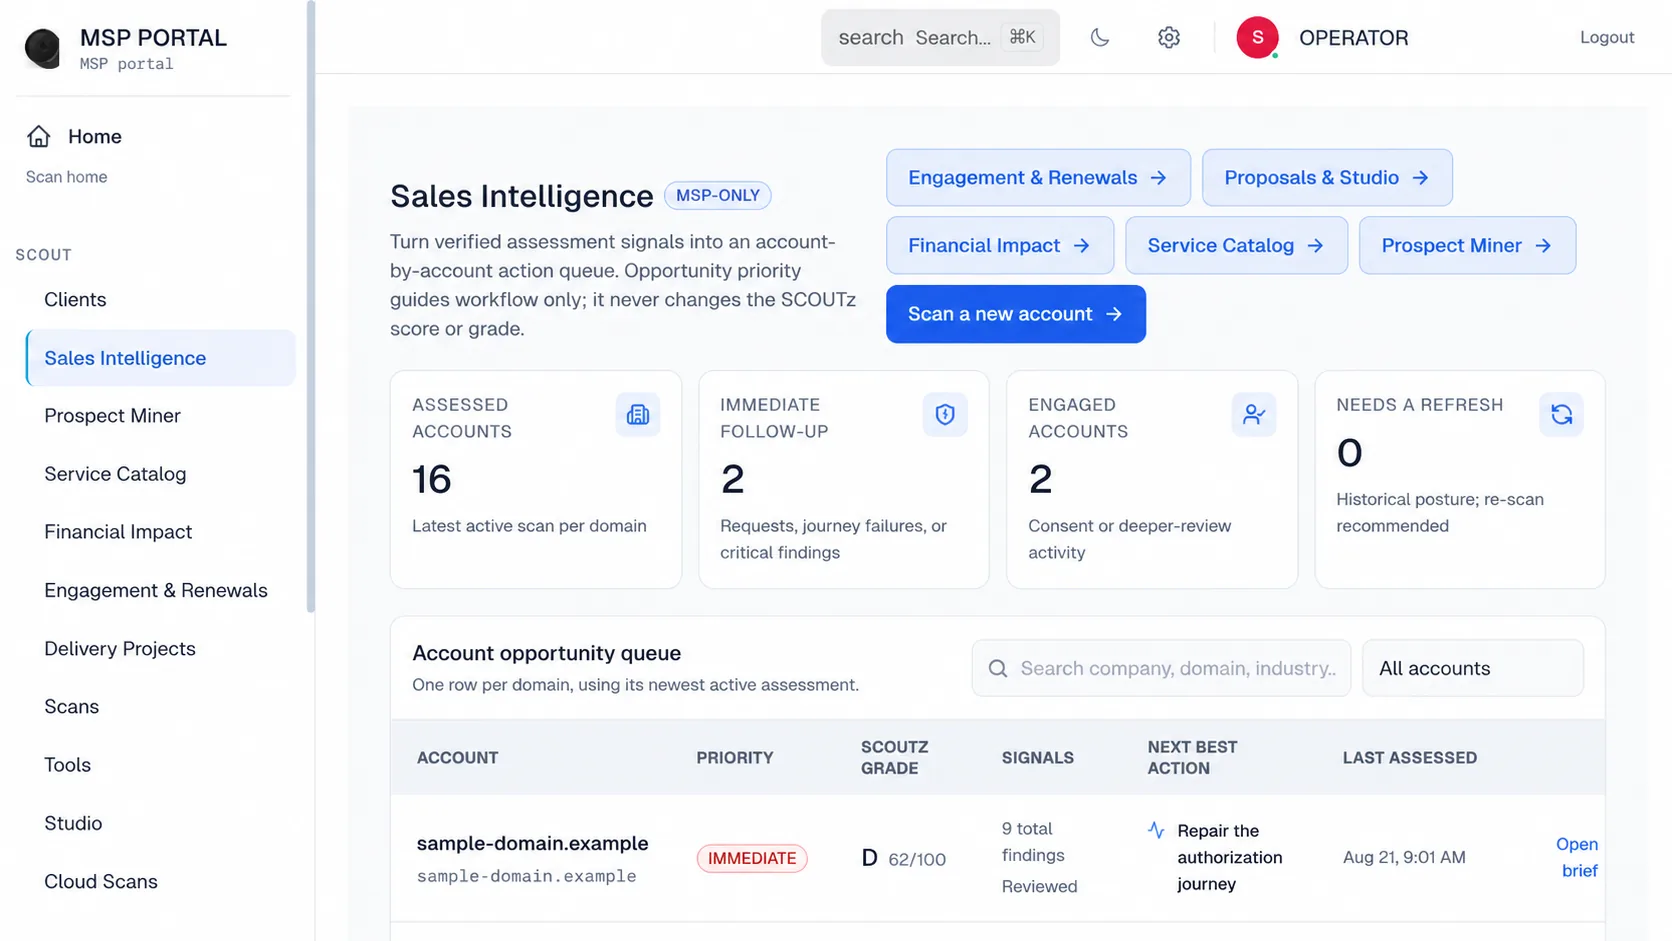
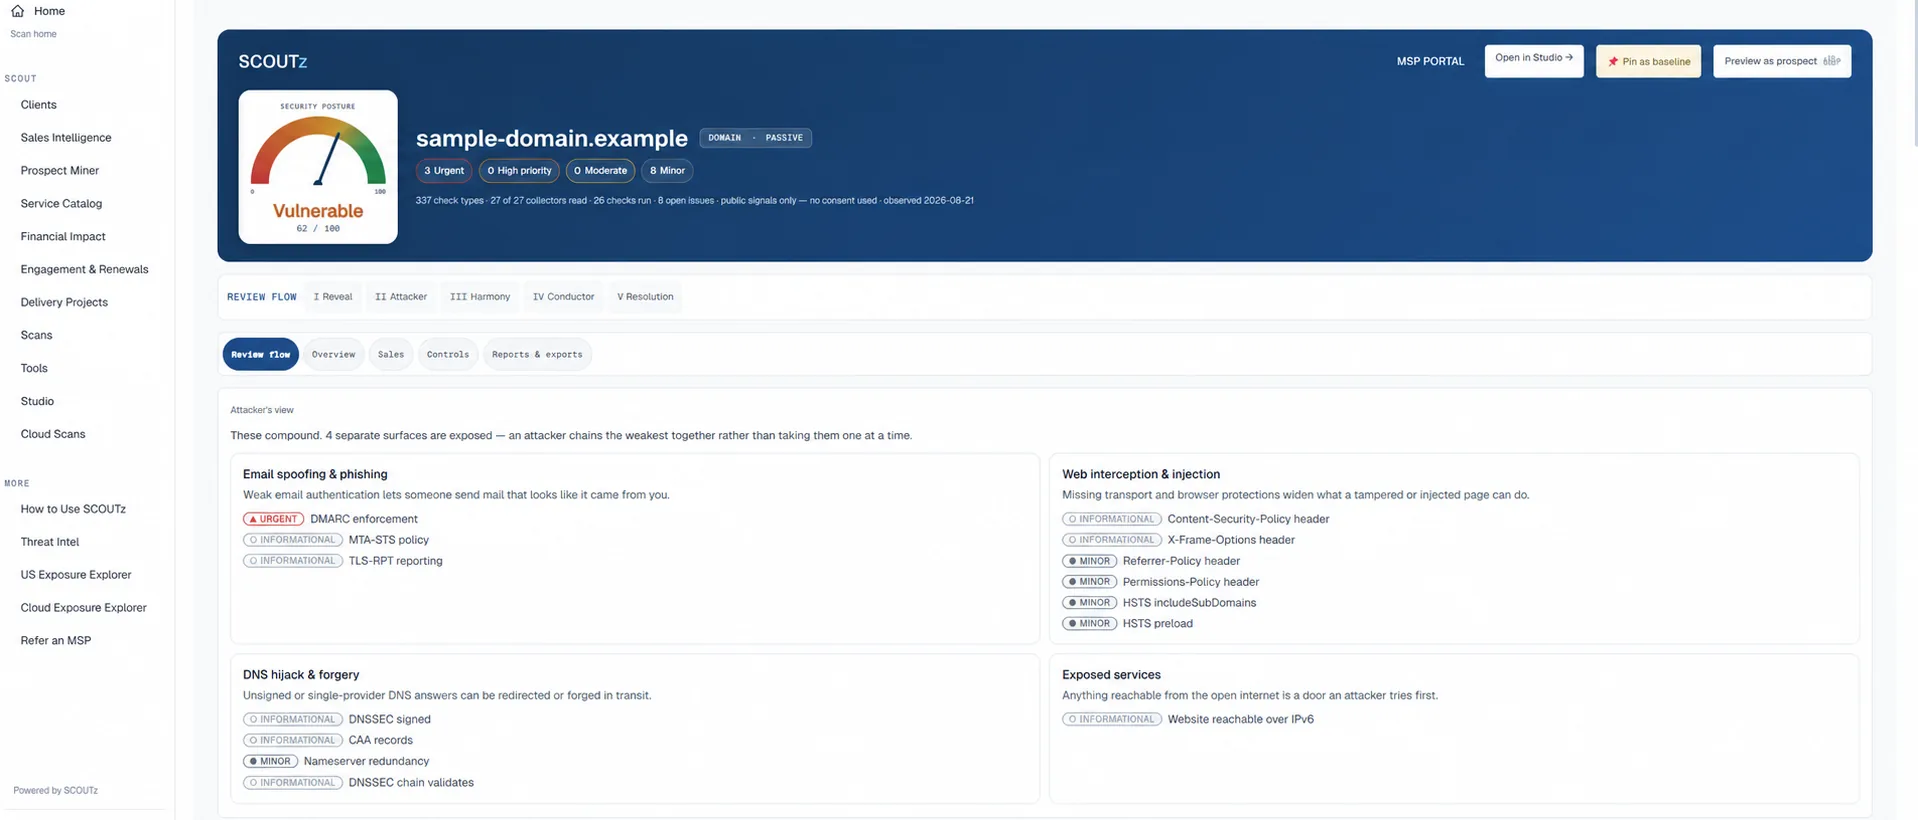
EVIDENCEWhat ranINSIGHTWhy nowPROOFWhat changed
READ-ONLY REVIEWNO AGENT OR INSTALLSOURCE-LABELEDMSP-OWNED ACTIONRE-VERIFIABLE
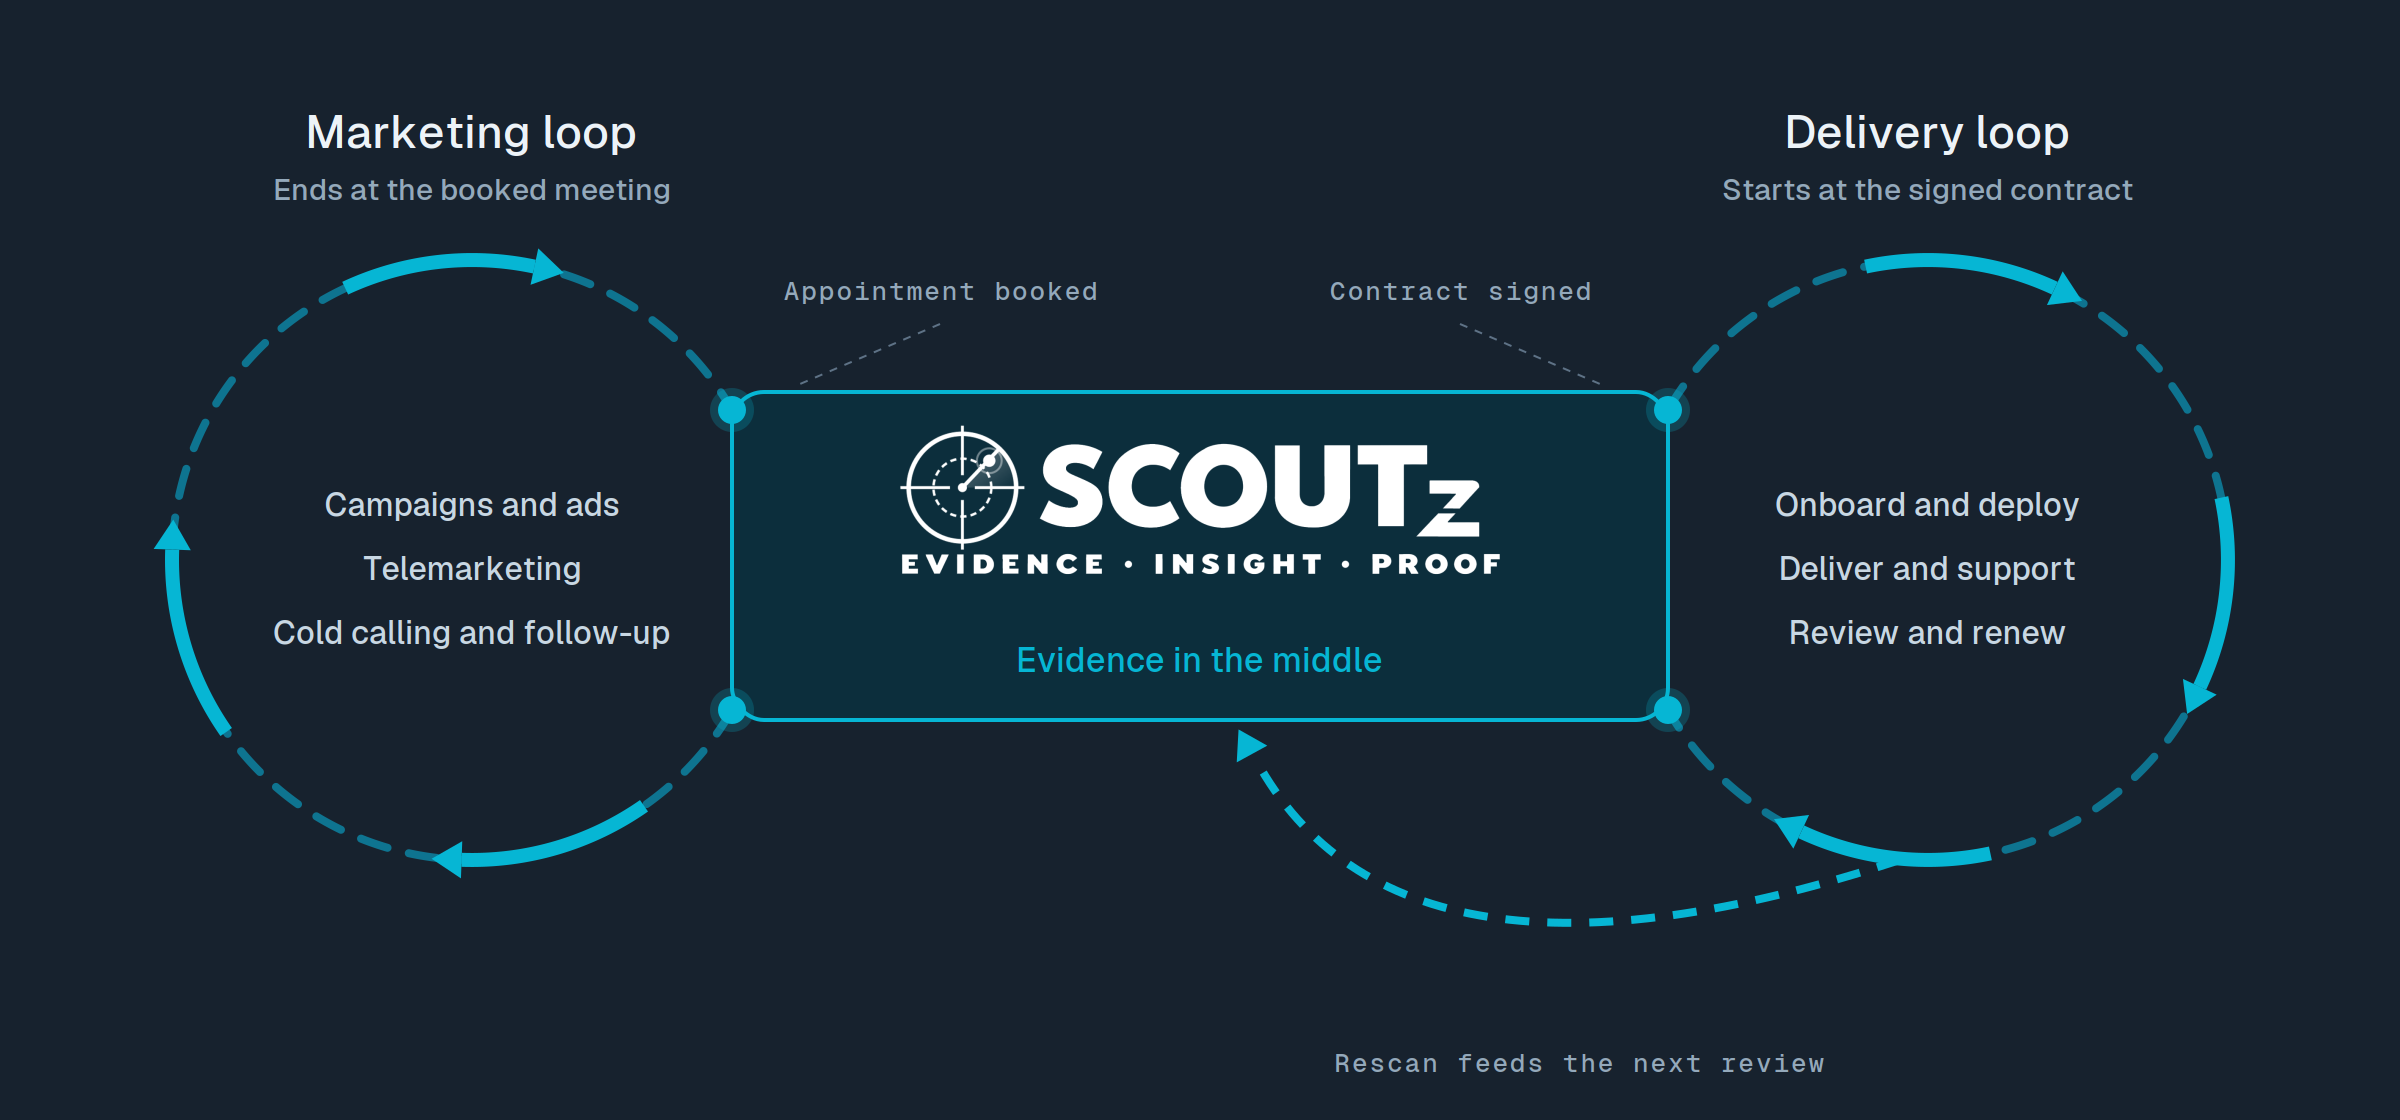
THE PART BETWEEN A BOOKED MEETING AND A SIGNED CLIENT
The missing middle of MSP sales.
A lead-generation partner may get you into the room. SCOUTz supports the preparation between a booked meeting and the next decision. Keep sourced findings, limits and questions together; the MSP owns the relationship and sale.
SCOUTz
Equip a better conversation.
Explore prospect intelligence →SCOUTz + MSP SALES
Earn the relationship.
Follow the journey →MSP OPERATIONAL STACK
Deliver the outcome.
See the handoff →What is MSP Prospect Intelligence?
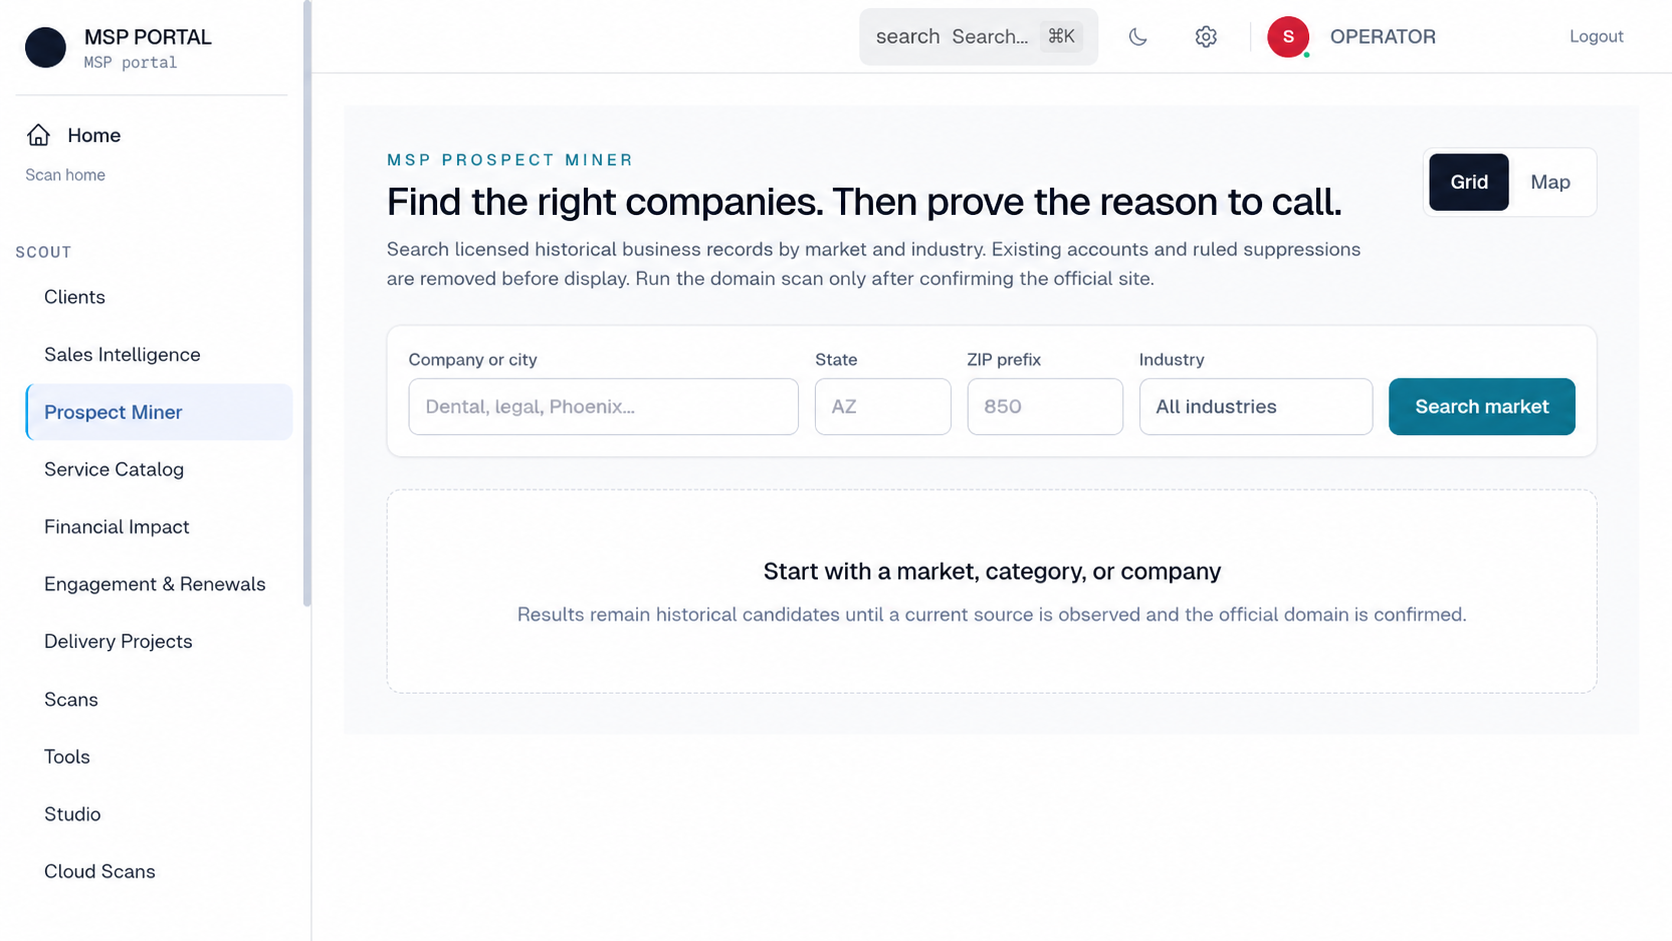
MSP prospect intelligence is the dated evidence and account context an MSP brings into a sales conversation, so discovery starts with what you already know about the prospect.
Read the category definition →LEAD WITH FINDINGS
The access layer changes what SCOUTz can tell you.
Public evidence earns the conversation. Customer-approved read-only cloud evidence deepens it. Fusion and correlation then connect separate observations into a route an MSP can explain and own.
Published records only. It does not see inside a cloud tenant.
Includes the public-domain roster, then adds supported tenant evidence.
ABOVE COLLECTOR OUTPUTFusion + correlation
Routes and relationships connect separate observations into a question an MSP can own. This is why the platform total is more than a collector count.
601platform finding types538 registered check IDs
"Saw you're hiring. Thought I'd reach out."
A public event is context for a question, not proof of a need or buying intent.
SCOUTz turns dated public-source observations and customer-approved Microsoft 365 evidence into a clearer conversation: what was found, what it might mean and what to ask next.
Public-domain observations establish selected published conditions, not delivered fraud, breach losses or buying intent.
Keep the observation, uncertainty and next question together.
A published DMARC policy requests monitoring only.
The intended enforcement and reporting process needs clarification—not a claim of compromise.
“Who reviews the reports, and is monitoring-only still the intended policy?”
Review the source and its limits. Bring a useful question.
HOW IT WORKS
Evidence before the meeting. Insight in it. Proof after.
Findings cite the check that produced them and the date it ran.
The domain review reads public records from outside. Anything a check could not read is marked unknown.
The evidence becomes a reason to talk to this account now and the questions to ask when you do.
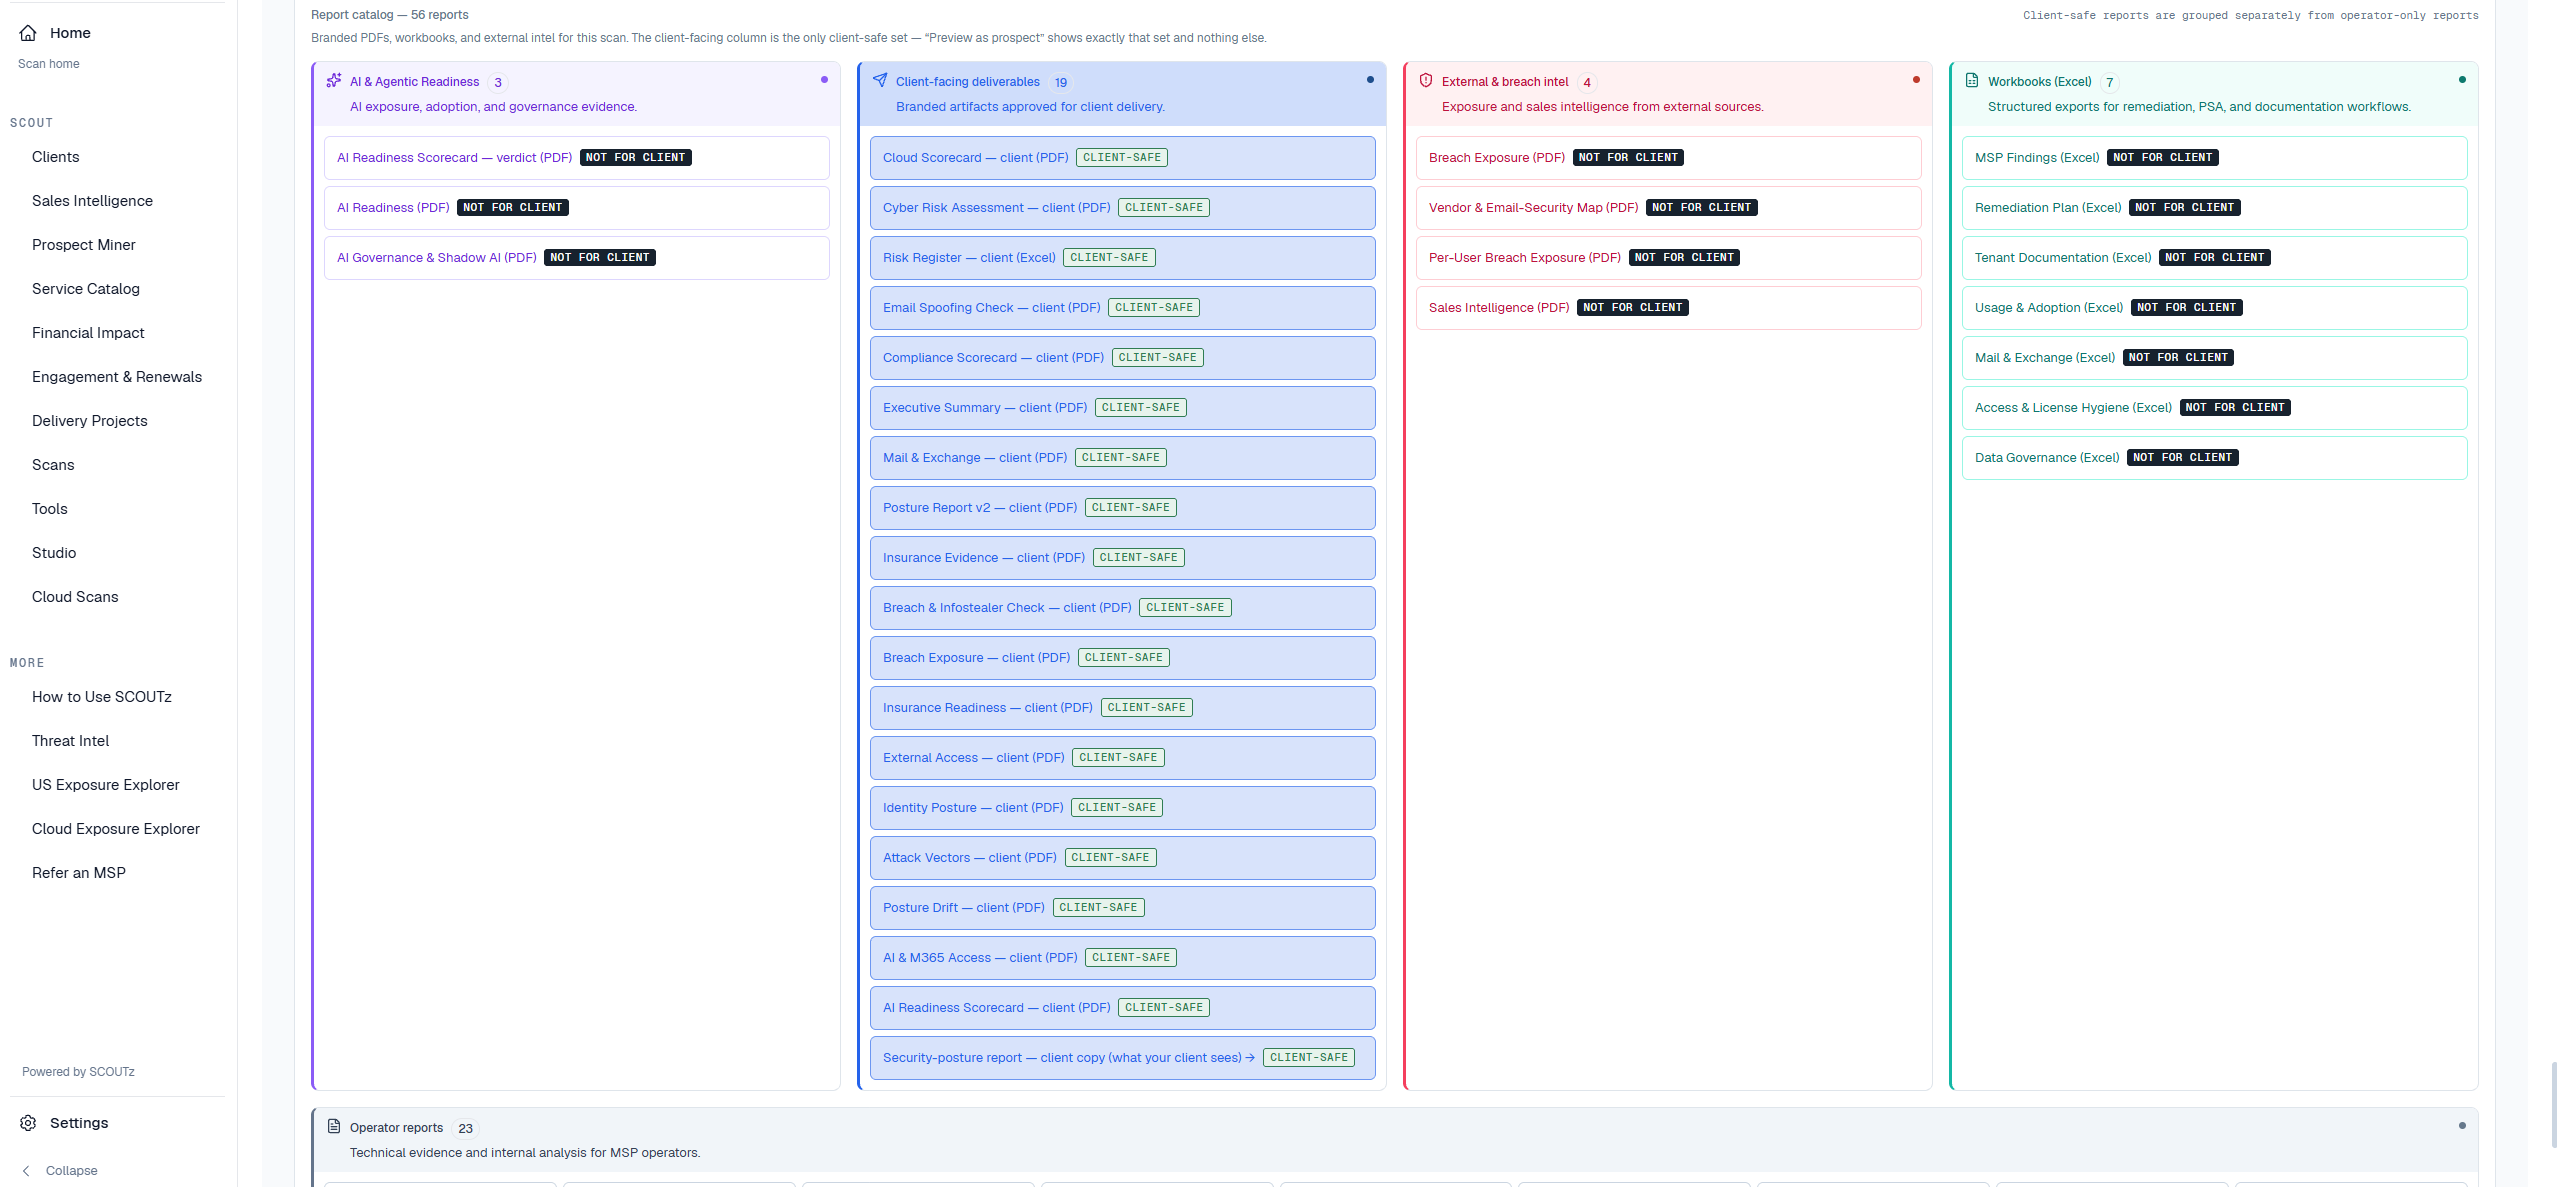
The owner gets a plain-language report under your brand. Your technicians get the operator edition.
With read-only consent, the Microsoft 365 review goes deeper and a rescan against the pinned baseline shows what changed.
Fix guides and a work plan turn findings into owned work before the next QBR.
EVIDENCE
An unknown never scores as clean.
Findings cite the check that produced them and the date it ran. Findings carry fix guides with prerequisites, steps, validation and rollback, a work plan the MSP owns, and ticket-ready text for the PSA. A rescan compares new evidence against a pinned baseline, so the next quarterly review rests on what changed.
Seen in a disclosed source.
Context, not purchase intent.
A hypothesis to validate.
Never scored as clean.
THE EVIDENCE LAYER
The record, the state, and the route stay together.
Every conclusion comes with the record it rests on.
The evidence page keeps published name servers, mail servers, sender and impersonation records, certificates, permitted certificate authorities, and discovered addresses separate from findings. It states what was read, without adding a verdict.
A short findings list is not a clean bill of health.
Every check resolves to verified working, needs attention, worth noting, or could not be read. Could not be read is never counted as a pass.
Findings can be correlated into an open route.
Named paths include certificate issuance, exposed surface, and invoice/payment fraud. SCOUTz correlates observed findings; it does not probe, simulate, or exploit.
Lead with findings, not scanners.
Collectors run: 35 · distinct findings they can produce: 123 for the public domain layer. With customer-approved read-only cloud access: 93 collectors · 370 distinct finding types. Platform-wide, 601 finding types across 91 emitting modules include fusion and correlation passes beyond collector output.
All 601 finding types carry authored business-language explanation, consequence, recommendation, and the evidence they were drawn from. The ledger separates 440 scored findings, 107 context observations, and 22 declared non-reads. Declared non-reads render under NOT ASSESSED THIS SCAN directly beneath the findings, so unread evidence is never mistaken for a pass.
EVIDENCE BEFORE FEAR
What SCOUTz won't do.
It won't model dollar losses from a breach that hasn't happened, and it won't blend platforms into one score. It also won't build the stolen-password slide. We can find it. We won't use it.
Deterministic checks decide whether a finding exists. AI helps write the explanation, and a person signs off on the claim. Every finding is a check that ran, on a date, not AI pretending a product exists.
Why stronger claims need stronger evidence →FROM MSP PARTNERS
"Man, I wish I had this in the meeting I just walked out of."
Zach Kinder, President and Partner, Net-Tech Consulting, El Paso, Texas
"I have done 2-3 discoveries now with it and am ready to use that data to put together the proposal presentations which are next week"
Tony Sollars, Watchtower IT
50 MSPs from 3 peer communities shaped SCOUTz in closed beta. They remain the SCOUTz founders group.
Telecom Reseller, September 10, 2026ChannelPro Network weekly roundup, September 11, 2026
Read the launch release →ONE SET OF EVIDENCE, TWO AUDIENCES
A report the owner can read, and one your technicians can work from.
Plain language, what was checked, what was found and when, and a next step for each finding.
Written for the business owner, under your brand.
The same evidence with more depth: fix guides, work plans, ticket-ready text, and any check that could not run marked unknown.
SCOUTz OPEN BETA
Run it against your next 3 prospects.
One MSP workspace, unlimited users. Unlimited prospect domain scans and Microsoft 365 reviews under fair use. Client-safe and operator reports under your brand, with rescans included. 30 days at $0 from provisioning, then $279/month.
- 01 · RegisterBusiness email, the workflow you want to prove first, and a card through Stripe. Nothing is charged today.
- 02 · ReviewA person confirms MSP fit and the right starting point. We reply within one business day.
- 03 · ProvisionYour workspace goes live with a sign-in link. The 30 days start here.
- 04 · Conversion3 days before anything is charged, we email the price, the charge date, and how to cancel.